⭐ Most Read
The Big Lie in Mobile Privacy (And How We Fixed It)
Why tapping 'Reject All' on Android apps doesn't always stop data collection, and how CookiePrime is fixing the root of the problem.
Read More →Your consent data stays in your infrastructure. Your cloud account, your database, your encryption keys. No vendor lock-in.
Built-in support for data localization laws including GDPR, CCPA, PDPL, and other regional requirements.
Switch providers anytime without data migration. Your consent data always belongs to you.
Why tapping 'Reject All' on Android apps doesn't always stop data collection, and how CookiePrime is fixing the root of the problem.
Read More →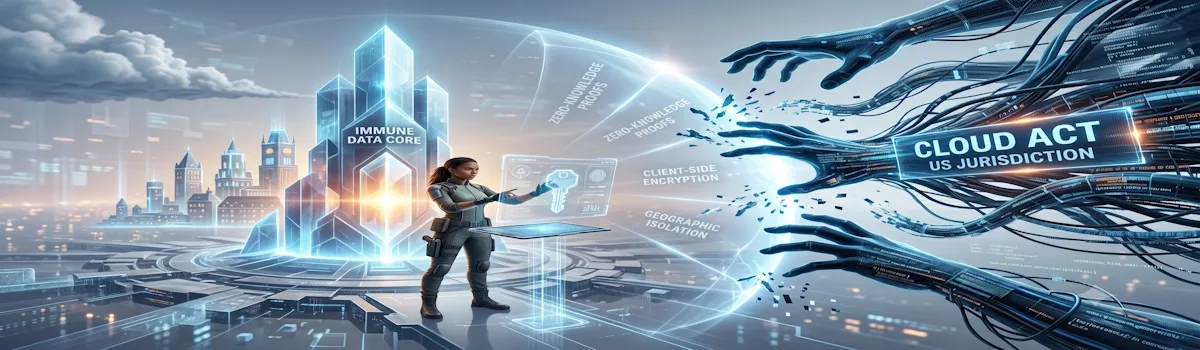
A deep dive into the architectural flaws of traditional CMPs and how CookiePrime built a CLOUD Act-immune, BYOD consent SDK.
Read More →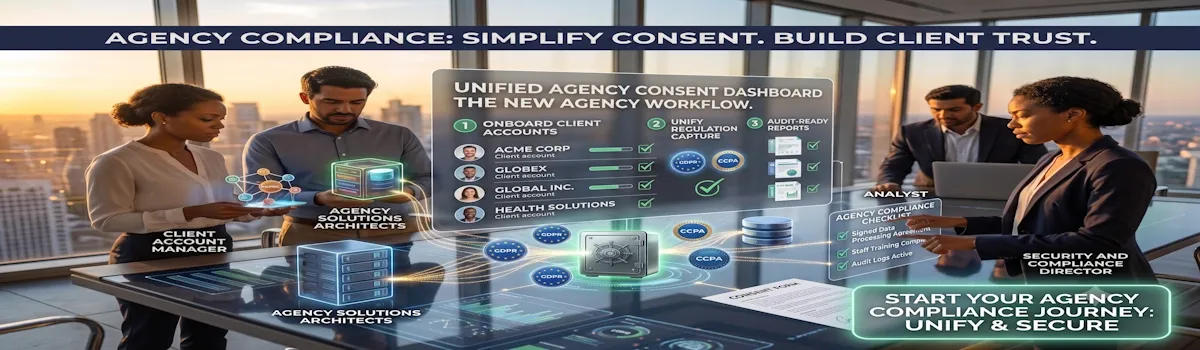
Why traditional CMPs fail digital agencies and how CookiePrime's Agency Partner Pack turns privacy compliance into a profit center.
Read More →
Privacy and copyright laws are written with extraterritorial reach. Learn how data retention policies, cryptographic hashing, and automated takedowns keep your AI infrastructure compliant globally.
Read More →
A common misconception about AI proxies is that they rely on LLMs to detect sensitive data. Here is a step-by-step breakdown of how AIGuard tokenizes data locally before it ever reaches external APIs.
Read More →
Adding GPTBot to your robots.txt is a good first step, but it won't actually protect your server. Here is the difference between passive legal boundaries and active firewall enforcement.
Read More →