In the modern enterprise tech stack, data privacy compliance has evolved from a checkbox item managed by legal departments into a core architectural challenge for engineering teams. With the global enforcement of strict data frameworks — ranging from Europe's GDPR to the Swiss LPD, Brazil's LGPD, and Saudi Arabia's PDPL — the stakes for mishandling user data have never been higher.
Yet, as engineering organizations deploy traditional Consent Management Platforms (CMPs) to solve this problem, they are inadvertently introducing a massive security bottleneck and a compliance backdoor: the U.S. CLOUD Act.
Most standard compliance platforms operate on a centralized SaaS model. They intercept tracking scripts, but they store the resulting cryptographic consent logs and audit trails on their own servers. Under the extraterritorial reach of the CLOUD Act, any cloud provider under U.S. jurisdiction can be legally forced to hand over data, regardless of whether the physical servers reside in Europe, the Middle East, or Asia.
For financial institutions, large-scale agencies, and enterprises handling highly confidential data, this centralized dependency means losing true data sovereignty.
Decentralizing the Compliance Layer: The BYOD Paradigm
At CookiePrime, our engineering and privacy teams approached this vulnerability by rethinking the relationship between the compliance engine and the storage layer.
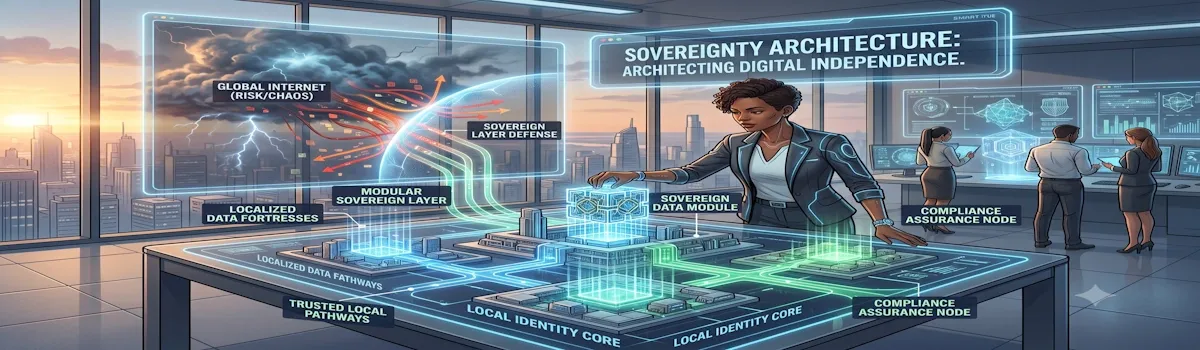
For our enterprise and business clients, we decoupled these environments entirely by pioneering a strict Bring Your Own Database (BYOD) architecture. Instead of routing consent records to a shared cloud, CookiePrime operates purely as a high-performance, on-device interception engine. The enterprise client connects their own secure, internal database to ingest and store the compliance logs.
Because absolutely zero user data ever touches or resides on CookiePrime's servers, the organization retains complete, exclusive custody over its legal proofs. This structural isolation effectively shields the enterprise from third-party data breaches and CLOUD Act exposure.
Engineering a 10-Minute Deployment
Achieving total data sovereignty shouldn't require exhausting development cycles or tanking app performance. We engineered CookiePrime to unify web and native mobile environments with a non-intrusive, zero-bloat codebase that deploys across any stack in under 10 minutes:
-
Sovereign Web Infrastructure: A single-line web script tag integrates seamlessly into custom builds (React, Node) and major enterprise e-commerce or CMS architectures (Shopify, WordPress, WooCommerce, BigCommerce, Wix). The engine automatically executes region-aware cookie scanning and script interception without manual configuration.
-
iOS Native Enforcement (Swift SDK): Traditional mobile privacy setups use clunky wrappers or network-level filtering that inject severe runtime latency. CookiePrime introduces Deferred Initialization for iOS. Tracking SDKs are safely held in an application-level queue and strictly checked at the call site. Third-party tracking blocks literally do not initialize until permission is granted, guaranteeing zero pre-consent data collection and ~0ms execution overhead.
-
Android Native Deep Scanning (Kotlin SDK): Our 420KB Kotlin library executes native, deep scanning directly on-device. It secures tracking payloads at the core level with zero local data retention.
Inspect the Core Mobile Codebase
True transparency is fundamental to secure architecture. To give development teams a direct look at our mobile enforcement pipeline, we have opened access to our compiled Android package and demo implementations.
Engineering teams can download the native .aar package, unlock a fully functional 30-day trial, and analyze two complete reference apps directly from our public repository:
🔗 Get the CookiePrime Android SDK on GitHub
Built for Global Operations
Operating globally requires an infrastructure that can adapt dynamically. CookiePrime features a built-in geo-awareness scanner that identifies a user's geographical region at the edge and enforces the corresponding legal framework automatically.
Furthermore, to eliminate the need for engineering teams to manage localization translation matrices, our interface handles global i18n out of the box. The platform natively supports all European languages, along with fully localized layouts for Arabic, Turkish, Hebrew, Korean, Indonesian, Thai, Japanese, and Traditional Chinese.
Own Your Privacy Stack
A compliance strategy is only as secure as the infrastructure supporting it. By shifting away from centralized data hoarding and moving toward a lightweight, sovereign model, enterprises can fully protect their user data without compromising application velocity.
Explore our live previews, documentation, and enterprise database models at CookiePrime.com.
For custom BYOD sovereignty deployments, enterprise licensing agreements, or technical consultations, connect directly with our dedicated engineering support team at: contact@cookieprime.com